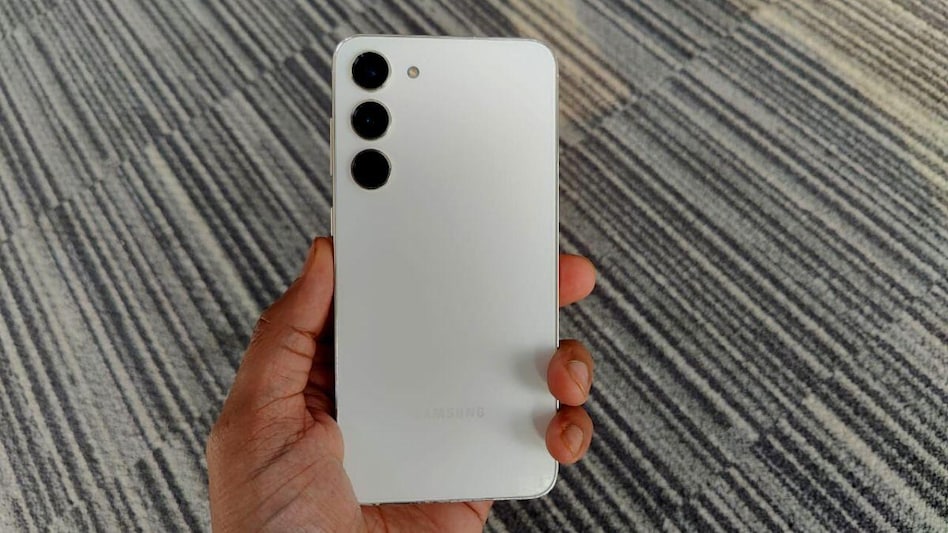
 Samsung Galaxy devices are impacted by this vulnerability
Security researchers at Google's Project Zero have discovered multiple 0-day vulnerabilities in Samsung Semiconductor's Exynos Modems, which can potentially allow remote code execution. Tim Willis, a researcher from Project Zero, has revealed that a total of 18 vulnerabilities have been discovered, with four of them being particularly severe.
These four vulnerabilities allow for Internet-to-baseband remote code execution, which means that an attacker can remotely compromise a device at the baseband level without the need for user interaction.

 Jio Platforms IPO fully subscribed within 100 minutes; QIB portion gets 3 times bids
 BT BIG STORY | No jobs, no security: The crisis facing India's educated youth
 Elon Musk plans a mega-merger? SpaceX and Tesla set up committees to explore merger deal
 ‘Everything everywhere at the highest quality…’: Akash Ambani on satellite broadband plan in India amid Jio IPO
 'Pretty close': After Rubio, Donald Trump says India-US trade deal is in sight
 Mohan Bhagwat On Regime Change Row: RSS Chief Targets Anti-CEC Protests | India Politics
 Marco Rubio In India: 26/11 Tribute, Jaishankar Talks & India-U.S. Trade Deal | Day 1
 Apple's New Smart Home Devices: HomeView, Apple TV 4K & HomePod mini 2 | Tech Today
 Starlink Vs India: Is Elon Musk Being Blocked? | Tech Today
 RBI Measures Boost Rupee | Is Further Depreciation Unlikely?

 Multibagger stock with 5,000% rally zooms 9% ahead of bonus issue record date, check details Jio Platforms IPO fully subscribed within 100 minutes; QIB portion gets 3 times bids
 Jio Platforms IPO subscribed 85% on Day 1; GMP hits fresh highs
 Kalpataru Projects shares rise 3% as subsidiary bags Rs 2,349-crore orders
 HD Fire IPO shares listing today: Check latest GMP before stock market debut
 Parents liable for children's participation, ₹21 lakh fine for violence: After Milan protests, Giorgia Meloni reads the riot actMultibagger stock with 5,000% rally zooms 9% ahead of bonus issue record date, check details
 Marco Rubio Meets Taj Security Head Who Was Present During 26/11 Mumbai Attacks
 Apple’s iPhone Duo screen has an unusually soft spot near the crease: Raises question on
 PSU Banks, IT, Digital Strong; Pharma Quiet